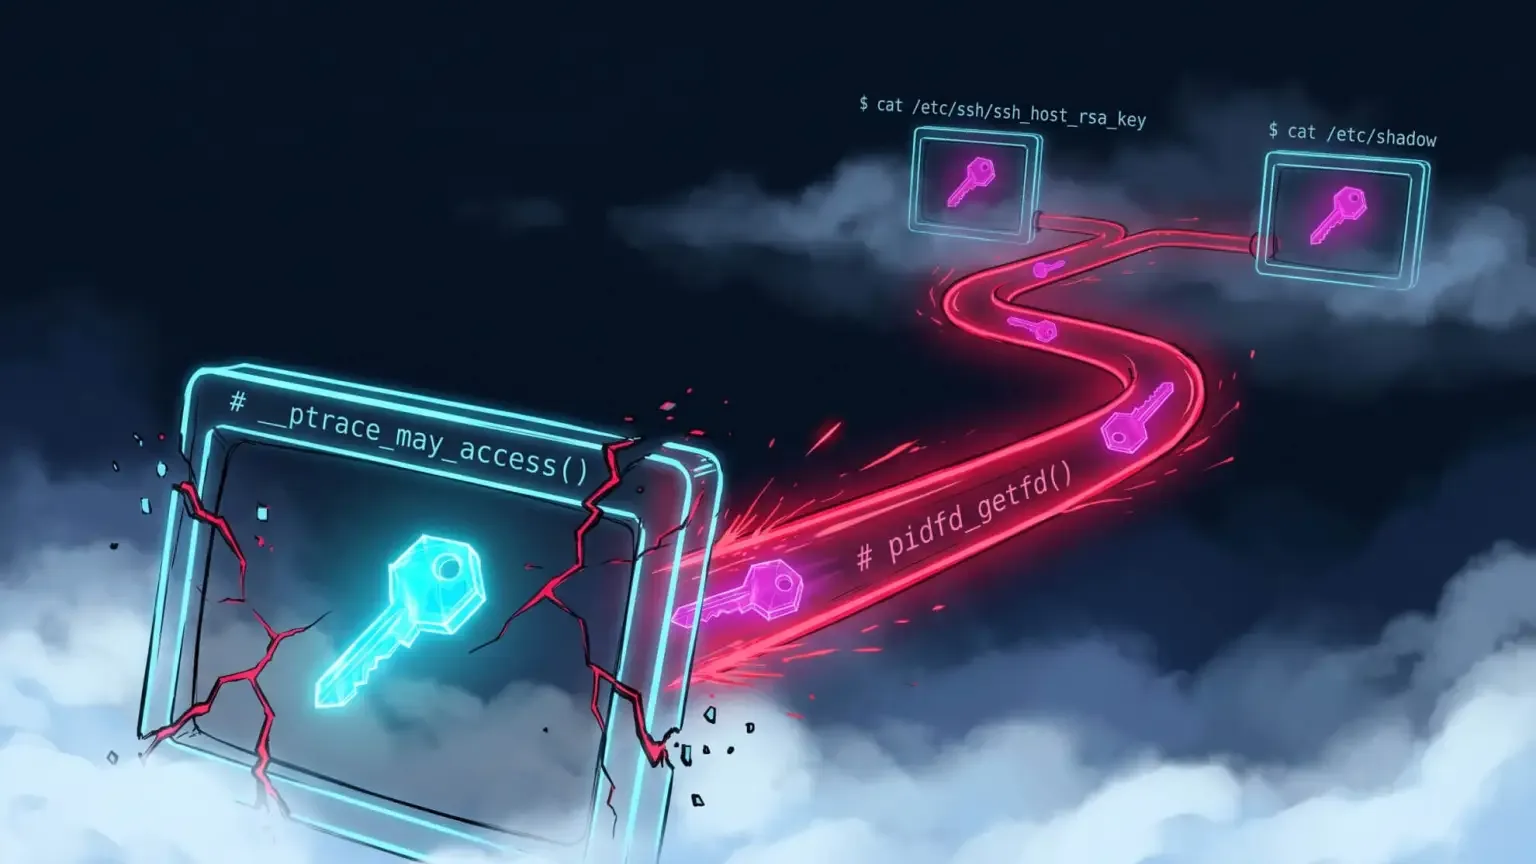


A newly disclosed flaw in the Linux kernel, the core software that manages a computer’s hardware and memory, allows code running inside a virtual machine to read memory on the physical host computer underneath it. The issue matters to cloud providers and any organization running untrusted workloads because the vulnerable networking code sits below individual cloud security settings.
How the PwnEscape Linux Vulnerability Works
Tracked as CVE-2026-99999 and nicknamed PwnEscape, the vulnerability resides in the Linux kernel’s networking stack rather than in a specific cloud provider’s software. Security advisories describe the flaw as a guest-to-host escape affecting Kernel-based Virtual Machine (KVM), a common Linux technology used to run isolated virtual computers.
An attacker with code execution inside a guest virtual machine can trigger the bug by sending specially crafted network packets. Beyond exposing host memory, reports indicate the flaw could cause the host machine to crash or potentially allow code execution on the host.
What the Vercel Sandbox Demonstration Showed
Security researcher Paulos Yibelo of pwn.ai discovered the PwnEscape Linux vulnerability during a security challenge hosted by cloud platform Vercel. Yibelo demonstrated the memory leak from inside a virtual machine running in Vercel’s live cloud sandboxes, which are isolated environments designed to run untrusted code safely.
Vercel confirmed the vulnerability after Yibelo reported it privately. Available reporting indicates no evidence that malicious actors have exploited the flaw in the wild or compromised Vercel customer data.
Why Cloud Customers and Operators Should Care
Virtual machines are built to keep different customers and workloads strictly separated on shared hardware. When a guest virtual machine can read host memory, it may expose sensitive data held by the underlying server, such as authentication tokens, credentials, process data, or information belonging to other workloads on the same machine.
This disclosure does not mean every Linux server or cloud account has been compromised. Actual risk depends on whether an environment uses an affected kernel version, how its virtualization networking is configured, and whether an attacker can already run code inside a guest virtual machine.
Upstream Patch and Remediation Status
Red Hat engineer Michael S. Tsirkin authored the upstream fix, which has been merged into the mainline Linux kernel as commit 6785011f8b16. The patch introduces a validation helper function named ip_check_csum_start() in include/net/ip.h and applies it across five affected networking paths, including IPv4 output fragmentation, bridge fragmentation, netfilter, and XFRM packet transformation paths.
Because enterprise Linux distributions manage their own kernel packages and backport fixes on their own schedules, administrators should rely on official vendor advisories rather than applying the raw mainline commit directly.
Practical Response Steps for Administrators
Infrastructure teams and virtualization operators should take the following steps to secure their hosts:
- Check security advisories from your Linux distribution, cloud provider, or virtualization vendor for updates addressing CVE-2026-99999.
- Apply updated kernel packages or host-side mitigations as soon as your vendor releases them.
- Reboot patched host systems when required so the updated kernel takes effect in memory.
- Audit which services allow external users to run arbitrary or untrusted code inside virtual machines or sandboxes, and restrict that access until hosts are patched.
- Monitor host logs for unexpected virtual machine crashes, abnormal network packet errors, or unexplained host instability.
Frequently Asked Questions
What is PwnEscape?
PwnEscape is the nickname for CVE-2026-99999, a Linux kernel networking vulnerability that allows a guest virtual machine to read memory from the underlying host system.
Does PwnEscape let a VM escape to the host?
Security reports classify the flaw as a guest-to-host KVM escape because it breaks memory isolation between the guest and the host. While researchers have demonstrated host-memory reading, reports also note the potential for host crashes and host code execution.
Was Vercel breached?
No. A researcher demonstrated the vulnerability against Vercel’s live cloud sandboxes during a security challenge and reported it privately. There is no reported evidence of real-world exploitation or exposed customer data.
Is this a Vercel-specific vulnerability?
No. The flaw exists in the upstream Linux kernel networking stack. Vercel was simply the environment used to test and confirm the behaviour.
What is the reported upstream fix?
The mainline Linux fix is commit 6785011f8b16, which adds the ip_check_csum_start() helper across five networking paths. Administrators should wait for tested package updates from their Linux distribution vendor.
Next Steps
While CVE-2026-99999 is a serious virtualization isolation flaw, there is no sign of widespread exploitation. System administrators should identify any Linux hosts running virtual machines or sandboxes, track their distribution vendor’s advisory for CVE-2026-99999, and schedule a maintenance window to patch and reboot affected hosts as soon as fixed packages arrive.